How Automation World Avoids Becoming a Watering Hole
Update: The article below was originally posted on March 28, 2018. In light of a recent The Wall Street Journal report outlining how trade publications have been used as watering holes to infiltrate industry, we felt it important to update our article with additional information. The original article outlines how Automation World protects its sites and visitors from malware attacks. Following the publication of the report from The Wall Street Journal , I spoke with our IT Director Andy Lomasky and he provided additional information about how we continue to protect our sites. According to Lomasky, there are four key steps we take in addition to the information listed below in the orginal article:
- Implementation of an enhanced password policy which requires all logins to our websites to have passwords of sufficient length and complexity to make it more difficult for hackers to “break in” to our accounts.
- Implementation of a software module that allows us to monitor and protect against a brute force attack whereby a hacker would attempt to break a password by repeatedly trying a series of different passwords until one was successful. This allows us to lock out and block suspected hackers from logging into our websites when this type of activity is detected.
- The original article cites our use of Drupal security software for our websites. We continue to update thee modules and have also implemented additional Drupal-recommended security modules.
- Two-factor authentication is required on key services used to manage our sites.
*********************************************
Original article published in March 2018:
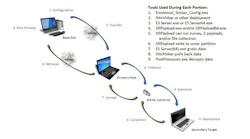
United States Computer Emergency Readiness Team (US-CERT) Alert TA18-074A details Russian government actions targeting U.S. government entities, as well as organizations in energy, nuclear, commercial facilities, water, aviation and critical manufacturing sectors. It explains, in part, how Russian government cyber actors gained access to industrial networks via the use of spear-phishing and watering holes.
As an industry media company, Automation World and its parent company PMMI Media Group (PMG), found the threat actors’ use of watering holes of particular interest. Here’s what the alert said about their use in the Russian attacks on U.S. industrial control systems (ICS):
“One of the threat actors’ primary uses for staging targets was to develop watering holes. Threat actors compromised the infrastructure of trusted organizations to reach intended targets. Approximately half of the known watering holes are trade publications and informational websites related to process control, ICS or critical infrastructure. Although these watering holes may host legitimate content developed by reputable organizations, the threat actors altered websites to contain and reference malicious content. The threat actors used legitimate credentials to access and directly modify the website content. The threat actors modified these websites by altering JavaScript and PHP files to request a file icon using Server Message Block (SMB) protocol from an IP address controlled by the threat actors. This request accomplishes a similar technique observed in the spear-phishing documents for credential harvesting. In one instance, the threat actors added a line of code into the file “header.php”, a legitimate PHP file that carried out the redirected traffic.”
Having learned about the watering hole issue from the CERT alert—and the specific reference to industrial trade media websites—I asked Dave Newcorn, senior vice president, Digital & Data at PMG, just how Automation World is protecting itself against this threat.
“PMMI Media Group uses a multi-layer approach to thwart any attempts to use its sites as watering holes for cybersecurity attacks,” Newcorn said. “The first layer of protection is provided by our websites’ hosting company, Acquia. They provide our sites with a state-of-the-art monitoring system—the same system used to protect some of the largest sites on the Internet, such as the IRS site. This means that any intrusion attempts at the system level are constantly being monitored and defended against by Acquia’s expert team.”
A second layer of protection for PMG’s sites is provided by having Acquia manage the underlying operating system for PMG’s websites. “With their oversight of the OS, we know that we have the latest security patches installed to protect our sites,” said Newcorn.
The use of Drupal software for PMG’s websites provides a third layer of protection, according to Newcorn. “This software system has a dedicated security panel that constantly reviews the core software and its modules for any potential security issues. PMG regularly applies all updates published by Drupal to stay on top of the latest cures to any security issues that arise,” he said.
In reference to the specific threats highlighted in the CERT alert, Newcorn said “There does not appear to be a known issue with Drupal that hasn't already been covered in past updates, according to the Drupal security blog.”
About the Author
 David Greenfield
 Leaders Logo
Leaders relevant to this article: